Data security for AI.
Control what data your AI can reach, and inspect every prompt, response and tool call for sensitive data, across the agents you run, the agents and servers you host, and the AI your employees use. Over MCP, A2A and model APIs. One engine, validated DLP. All shipped.
Every AI touchpoint is a new insider.
Agents act on their own with standing access. Employees paste regulated data into public AI. Both reach for data all day — and the sensitive part is often in what comes back.
An insider that never sleeps.
An agent calls MCP tools, other agents and models on its own — with credentials you issued once and standing access you rarely revoke. One tool response carrying a patient record or a card number flows straight into the model's context, and onward.
A tab is an exfiltration path.
People move faster with AI, so regulated data lands in prompts and uploads across ChatGPT, Claude, Gemini and thousands of apps — most of which security never approved and can't see.
Gateways log that it happened. BlueAspen stops the data from leaving — by inspecting and redacting what AI brings back, in place, before it reaches the model, the agent, or the person.
One policy engine and one detection stack, on every path AI takes.
Whether the actor is an autonomous agent or a person, the same validated detection runs under one policy engine.
Not a PII checkbox. Built around the data.
AI gateways, MCP proxies and agent controls are shipping everywhere. The depth isn't: runtime enforcement that inspects and controls the data inline, at the moment of the call, on four axes a connection-first product doesn't do well.
Data, not traffic
- We inspect and redact what AI brings back — on the result leg, where the leak happens
- Redaction applied in place, so the reply stays valid and the AI keeps working
Audit-grade, not best-effort
- Validated detection — Luhn, NPI, IBAN, Shannon entropy — across 60+ context-scored patterns
- A reason on every finding, tuned for low false-block. A compliance artifact, not a guess
Fail-closed where it guards data
- On ingress and agent-to-tool paths, a call we can't judge never reaches the data
- A misconfigured gateway refuses to start. (Employee egress fails open by design — never block someone working.)
Find what's undeclared
- Agents, MCP servers and AI usage surfaced from the traffic itself
- Including the shadow ones no registry knows about
The data path, on one screen.
Every AI call, every finding, and every decision — with the rule that fired on each one.
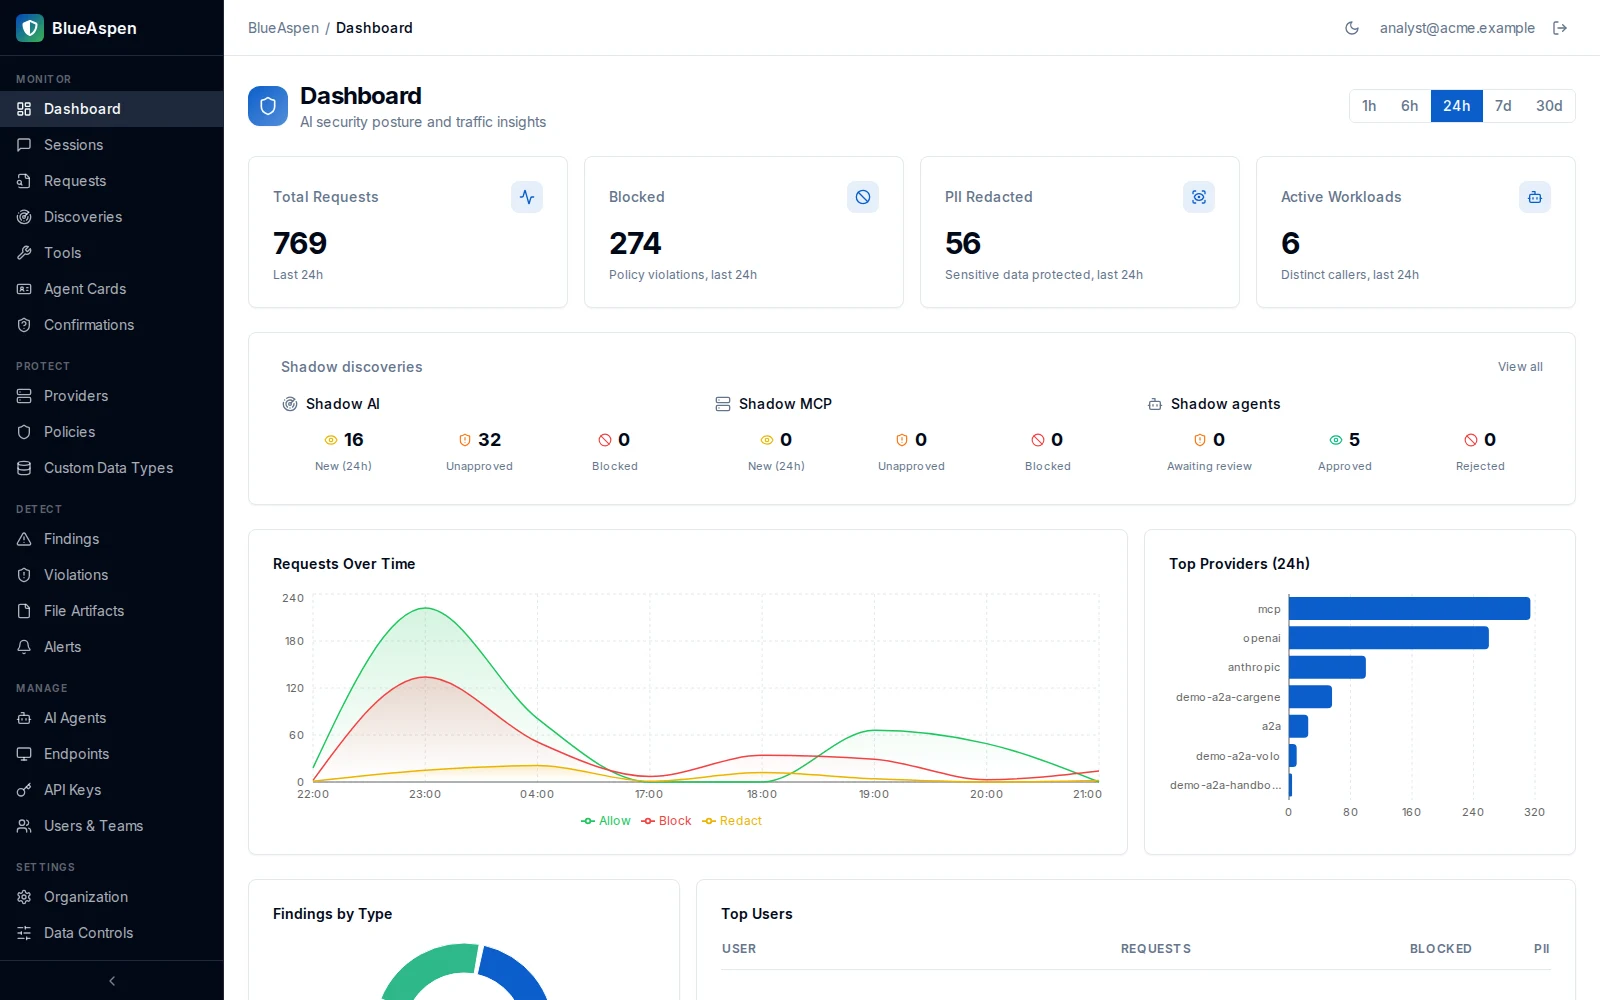
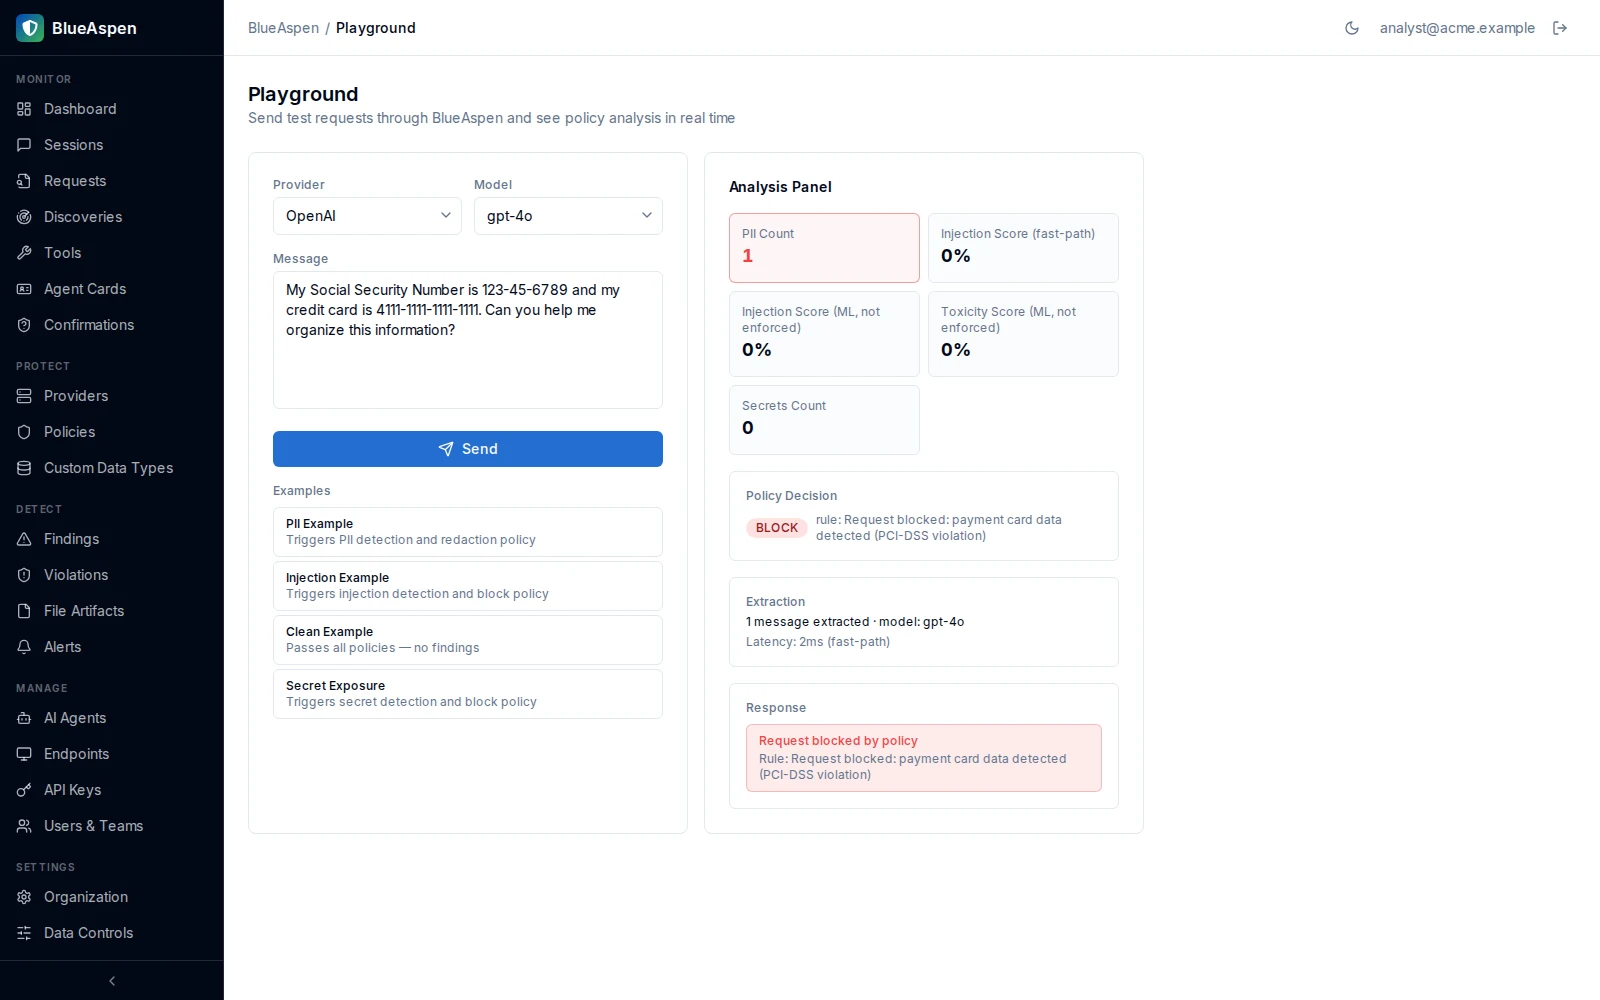
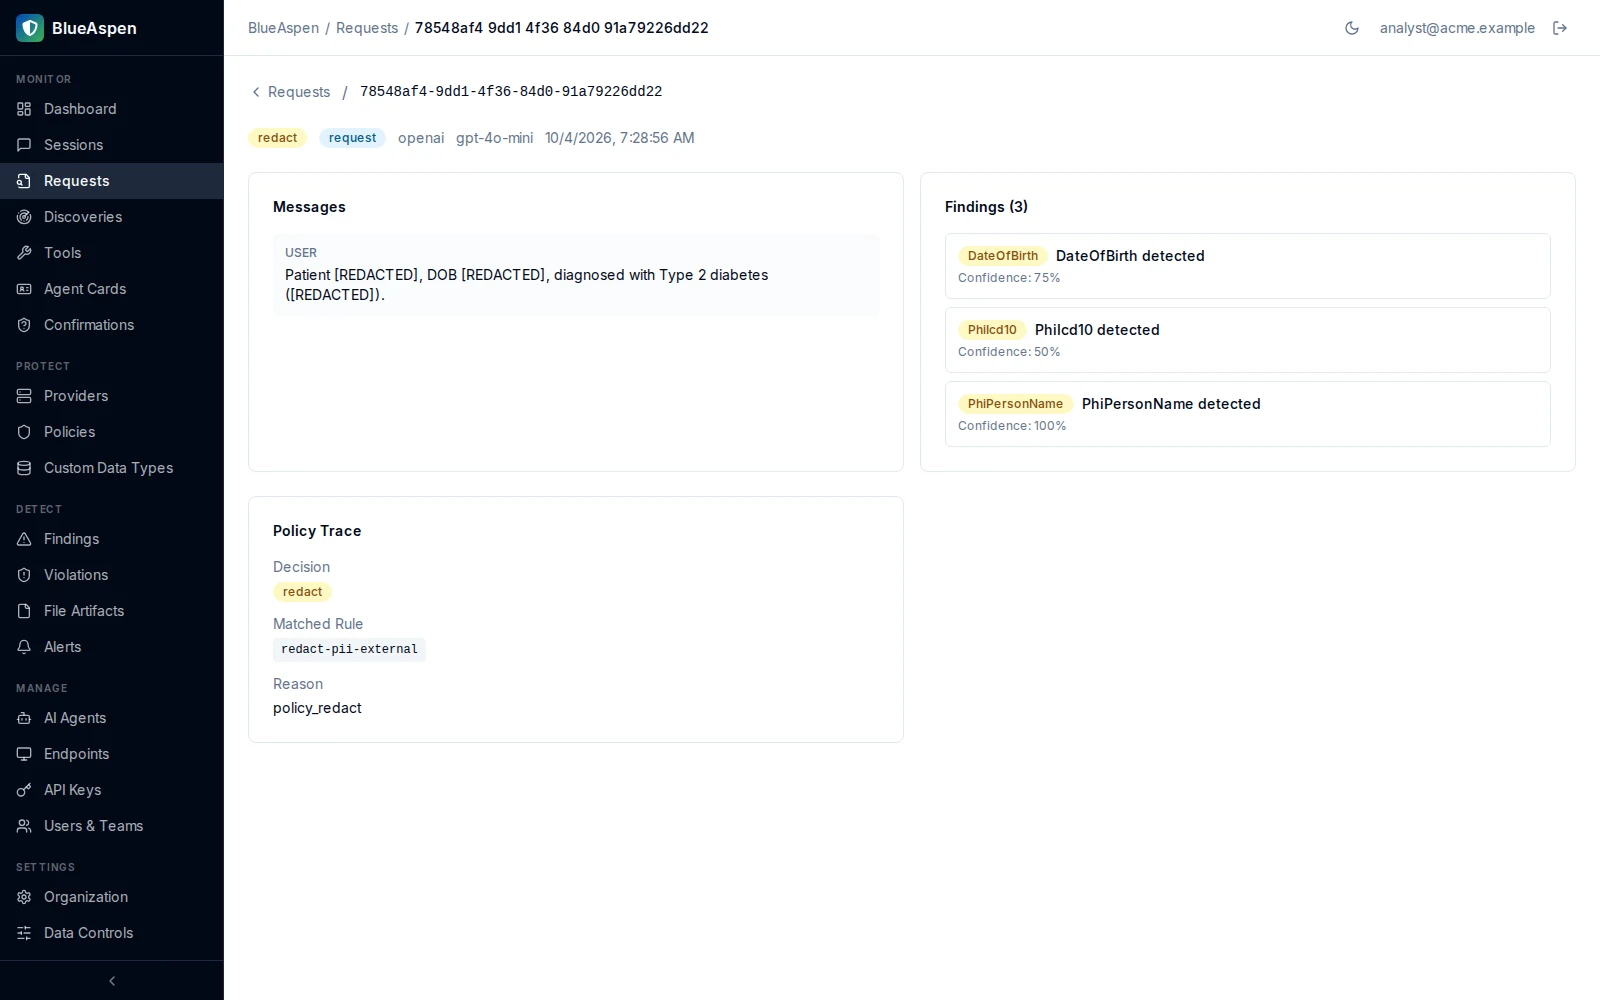
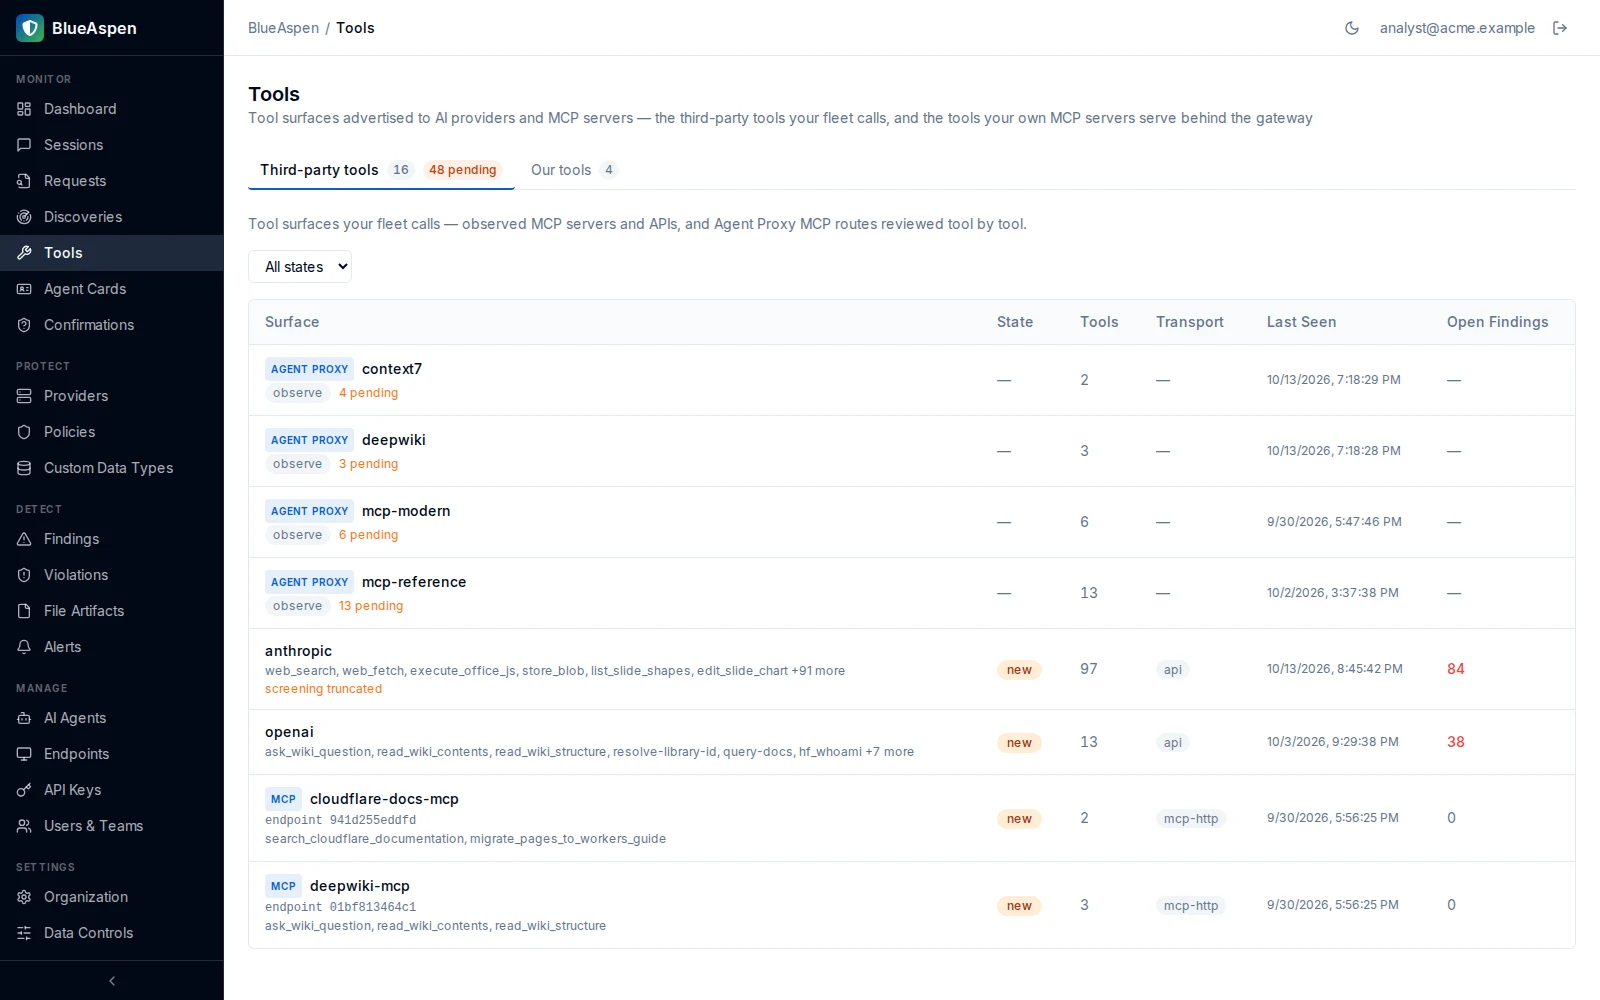
Screens from our live development environment, running synthetic test traffic.
We complement your stack — we don't replace it.
Your AI gateway & DLP / CASB
Route and log what AI does.
- Routing, fallbacks, cost control, caching, quotas
- Access, observability, request logging
- DLP on files, web and email
- Keep all of it — it's not our job
BlueAspen
Inspect and control what the data does.
- Validated DLP on the result leg, redacted in place
- Fail-closed on ingress — a call we can't judge never reaches your data
- Inside MCP, A2A and model traffic — where DLP/CASB can't reach
- Discovery of undeclared agents, MCP servers and AI use
Gateways route and log what AI does; BlueAspen inspects and controls what the data does. Deploy it alongside the AI gateway and the DLP/CASB you already run — on the data path.
Validated, not guessed.
A regex matches a shape. A validator proves it. We run the real check digits, so a finding is defensible and a non-match isn't a false alarm.
Take a 16-digit number. Any classifier can see “looks like a card.” BlueAspen runs the Luhn checksum the card network itself uses — one of these passes, one doesn't, and only the real card becomes a PCI finding.
- Luhn Credit-card and NPI check digits
- ABA Bank routing-number checksum
- mod-97 IBAN international account validation
- entropy Shannon-entropy gate for secrets and keys
- context Confidence scored on surrounding text, capped and explained
Shipped, verified, and in design-partner pilots.
Proof you can check, not logos — we're in design-partner pilots with regulated teams.
enforcement modes shipped
live end-to-end — A2A + AWS Bedrock
automated tests
validated patterns — PCI, HIPAA, PII, secrets
Fronts the MCP and A2A servers you expose.
Passes the official MCP client SDK against the reference server. The hosted A2A gateway passes 12/12 end-to-end.
Egress control for the agents you run.
MCP, agent-to-agent and model calls — 22/22 and 24/24 live end-to-end, including AWS Bedrock. Each agent reaches only what you granted it.
For people using AI.
40 providers and a ~6,000-domain catalogue. Prompts are blocked or redacted in place on ChatGPT and Claude, including Claude’s new app.
12 analyzers run on local ONNX models, so by default no customer data goes to a third-party LLM.
Founded by enterprise-security leaders (ex-Proofpoint, ex-Workday, ex-Teradata), bringing data-loss prevention to AI.
Research and perspectives on AI data security.
Short reads for security leaders navigating a category that's still being defined.